Slovakia finds Russian backdoor in traffic speed cameras
🚨 Risky Bulletin: Russian Backdoors Discovered in Slovakian Traffic Cameras
Newsletter Date: August 19, 2026
Author: Catalin Cimpanu, News Editor
Sponsor: Socket Security
🛡️ Primary Report: The NERO R-ONE Security Crisis
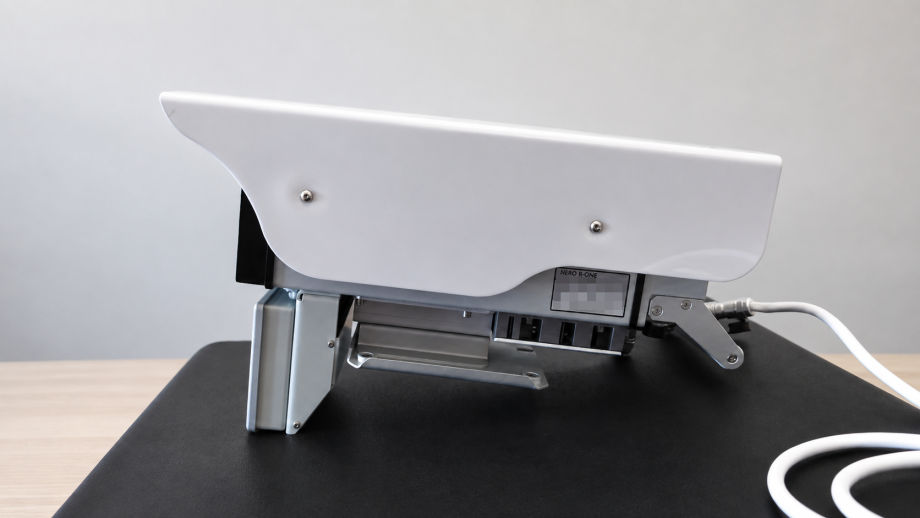
Slovakia's national security agency, the NBU, has issued a critical alert regarding the deployment of NERO R-ONE high-speed traffic cameras. The investigation reveals that these devices are not what they seem.
The Backdoor Mechanism
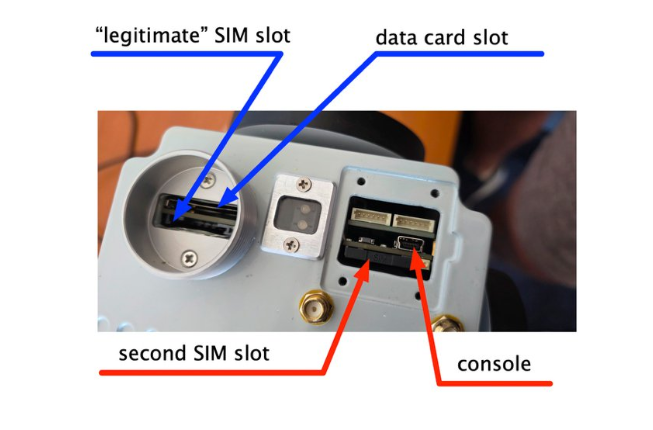
The NBU discovered a hidden backdoor that allows unauthorized actors to gain shell and network access to the cameras. This is triggered via a simple SMS message sent from a specific set of hardcoded Russian phone numbers.
Origin and Procurement
The cameras were purchased as part of a massive infrastructure overhaul.
- Project Budget: (EU-funded).
- Quantity: 279 units intended for installation by the Interior Ministry.
- True Identity: The NBU found these are actually rebranded
CORDON PRO.Mmodels, manufactured in Russia. - Controversy: The purchase was linked to a Cyprus-based shell company utilizing
legitimatefraudulent certifications.
Technical Vulnerabilities
Beyond the intentional backdoor, the NBU technical report highlighted several critical failures:
| Vulnerability | Detail | Risk Level |
|---|---|---|
| SecureBoot | Feature is disabled; firmware origin is not verified. | 🔴 High |
| Web Portal | Multiple security holes in the management interface. | 🟠 Medium |
| Live Streams | Broadcasts are exposed to anyone with the IP (no password). | 🔴 High |
Government Response
The Interior Ministry initially claimed that the cameras were not Russian and that the risk was negligible because the devices would operate on a "closed loop" network. However, following the report:
- Deployment of cameras has been paused.
- Independent auditor has been commissioned for a secondary assessment.
- Investigation into similar devices in Croatia and Eastern Europe.
🎙️ Risky Business Features
In the latest podcast episode, James Wilson interviews James Kettle (Director of Research at PortSwigger). They explore the intersection of AI and cybersecurity, specifically focusing on using Large Language Models (LLMs) to engineer entirely new attack vectors.
📉 Breaches, Hacks, and Security Incidents
Political & Governmental Targets
- UK Prime Minister: Andy Burnham was targeted by a scammer impersonating Susie Wiles (White House Chief of Staff). Burnham identified the fraud himself. This follows a pattern of targeting US officials via leaked contact lists.
- Ukraine's ARMA Agency: A cyberattack disrupted the agency responsible for managing seized Russian assets, specifically impacting the transition of management for the beverage company
IDS Ukraine. - Berlin City Government: Two major departments (Transport and Urban Development) suffered a hit that disabled emails and remote gateways.
- Action taken: IT staff isolated the agencies from the main city network.
Corporate & Institutional Leaks
- Baylor Genetics: A June breach exposed personal data of both employees and patients. The total number of victims remains undisclosed.
- UT San Antonio: Systems were taken offline over a weekend.
- Impact: Tuition deadlines extended; all user passwords must be reset.
- SafePal: Personal information of approximately 40,000 customers was stolen. This affected users who ordered hardware wallets during a specific window in May.
Critical Infrastructure & DDoS
- Winnipeg Health Sciences Centre: A ransomware attack disabled HVAC systems and electronic access doors.
- Status: Onsite security increased; clinical operations remain functional.
- BlueSky & GitHub: Both platforms were hit by DDoS attacks on Sunday and Monday by an Iranian hacktivist group.
Official Statement from BlueSky:
"Bluesky experienced a DDoS attack—a flood of junk traffic meant to knock servers offline—over a period of 24 hours. We have upgraded our defenses..."
🖼️ Gallery of Related Assets