Samsung TV privacy issues
Breaking Into the Living Room: Rooting a 2025 Samsung TV
A security researcher and reverse engineer known as @log4j recently shared their journey attempting to gain root shell access on a modern 2025 Samsung TV. While the goal was administrative control, the process revealed a staggering amount of embedded telemetry.

The Technical Barrier
The initial attempt to analyze the device involved reversing the firmware. However, the researcher hit a significant wall: the firmware is protected by AES encryption.
In mathematical terms, the firmware exists as a ciphertext , where: (Where is the AES encryption algorithm, is the secret key, and is the plaintext firmware).
Because the keys are not stored in an accessible software layer, the only way to retrieve them is through invasive hardware modification.
Hardware Requirements for Decryption
To bypass the encryption, one would need to:
- Physically disassemble the unit.
- Perform "magic" via
UART(Universal Asynchronous Receiver-Transmitter). - Utilize
JTAG(Joint Test Action Group) debugging interfaces.
The "Juicy" Discoveries
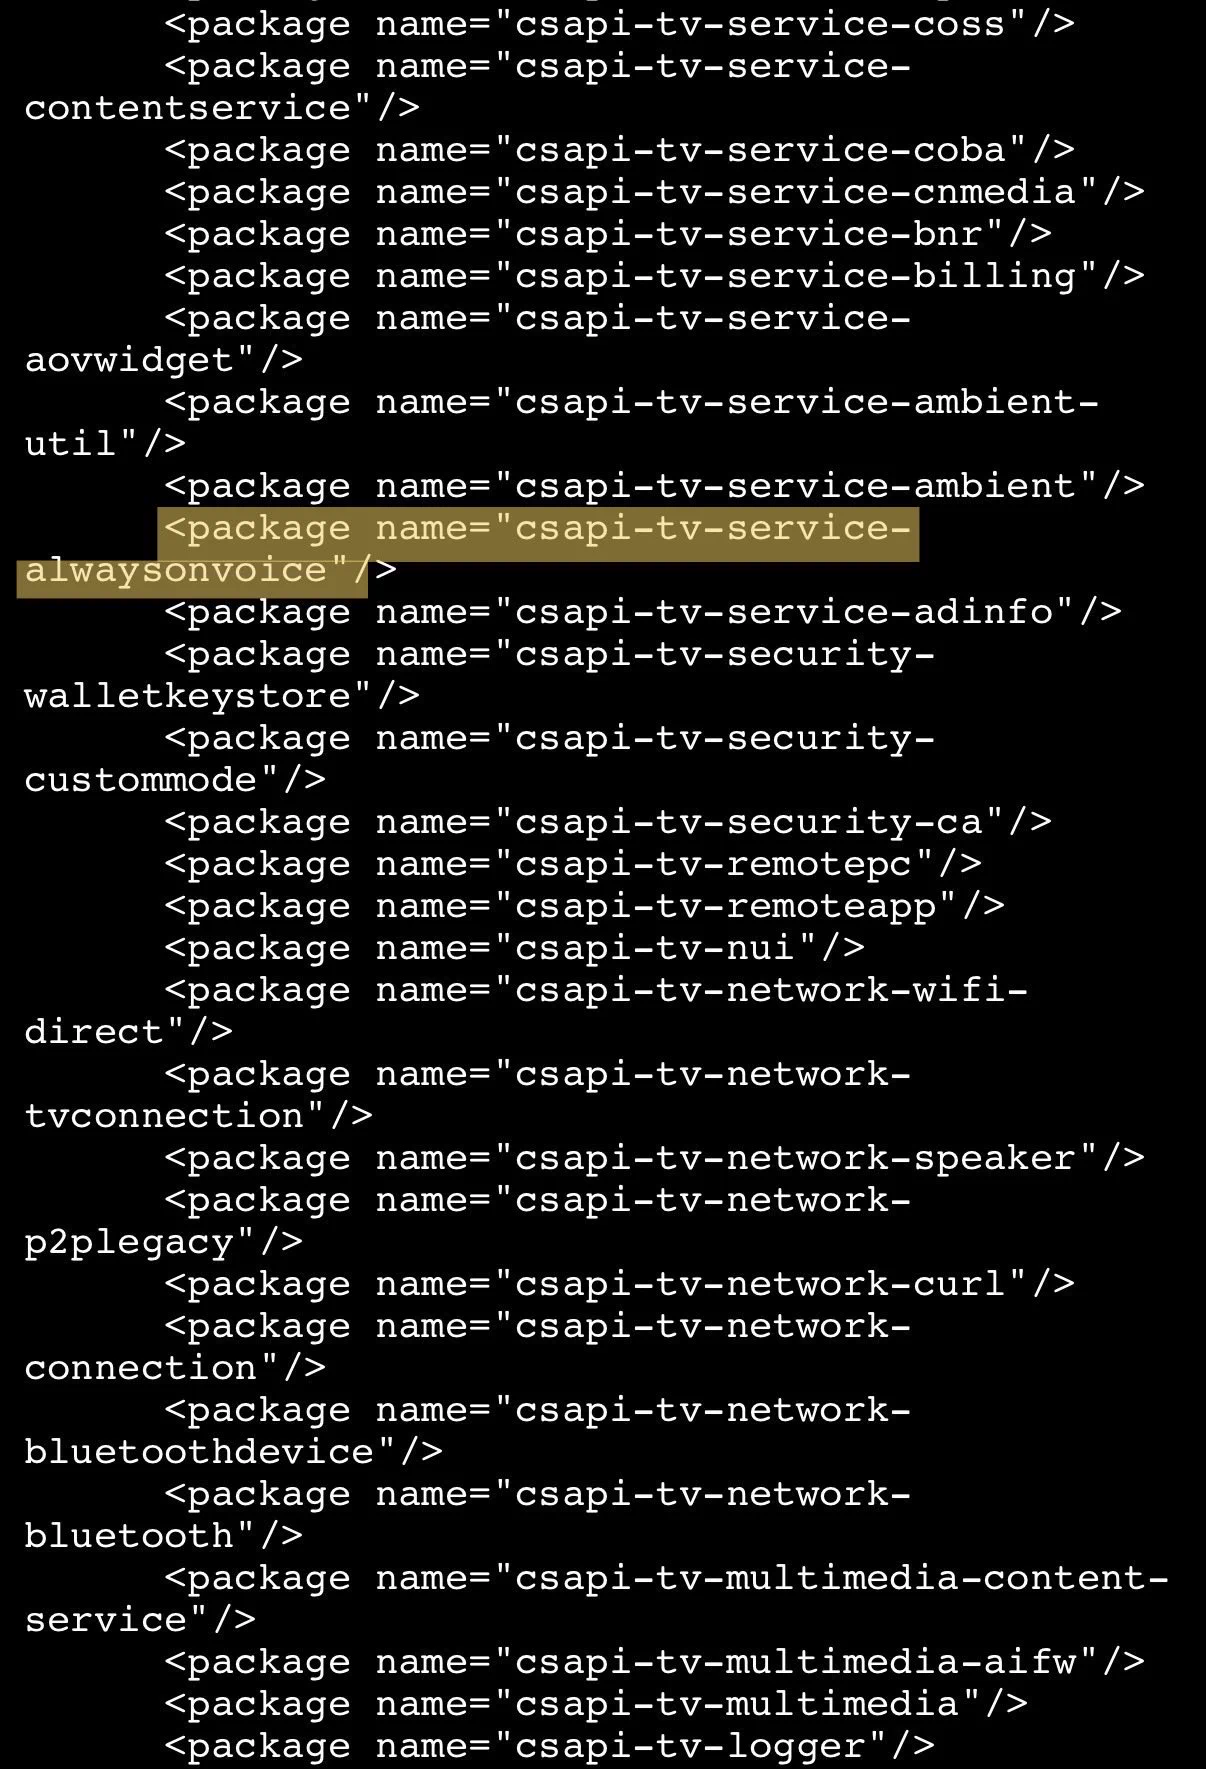
Once the system was probed, @log4j uncovered a suite of privacy-invasive features. The TV isn't just a display; it's a data collection hub.
"Always on hot mic functionality btw."
Telemetry Checklist
The researcher identified the following active services:
- Automatic Content Recognition (ACR)
- Geo-positioning tracking
- Network mapping
- Targeted advertising services
- User profile construction
- 4 distinct DRM services
- General telemetry streams

Community Reaction & Analysis
The findings were so significant that @log4j reached out to GamersNexus to see if the hardware community would be interested in a deeper dive.
Another user, @liminalsunset_, commented on the security architecture, noting that while Samsung claims the device is secured by Knox, the reality of the EL2 hypervisor implementation may be different than advertised.

Comparison: Samsung vs. LG
For enthusiasts who prioritize root access, the choice of hardware often comes down to the ease of modification.
| Feature | LG OLED | Samsung OLED |
|---|---|---|
| Root Accessibility | Historically easier | Difficult (AES/Knox) |
| Price Point | Standard | Often Cheaper |
| Privacy Concerns | High | Very High |
Final Thoughts
The ability to obtain root on a Samsung OLED is a game-changer for some. As one user noted, they previously stuck to LG OLEDs specifically for root access, but the lower price of Samsung OLEDs—combined with the possibility of rooting—makes them a more attractive, albeit more "nosy," option.
# Hypothetical root shell access
# user@samsung-tv:~$
# sudo su -
# root@samsung-tv:~# [Telemetry Disabled]